Task Overview
John the Ripper एक password-cracking tool है। आसान भाषा में समझें तो अगर हमारे पास किसी encrypted file का password नहीं है, तो John एक wordlist में मौजूद अलग-अलग passwords को एक-एक करके try करता है। GPG file के मामले में पहले gpg2john की मदद से encrypted file को ऐसे hash format में convert किया जाता है जिसे John समझ सके। इसके बाद John उस hash को wordlist के passwords के साथ match करके सही password खोजने की कोशिश करता है।
question-
Find an encrypted file called personal.txt.gpg and a wordlist called data.txt. Use tac to reverse the wordlist before brute-forcing it against the encrypted file.
Step 1: SSH & File Discovery
Log in via SSH and locate the required files on the remote server:
sarah@james:~$ find / -type f -name personal.txt.gpg 2>/dev/null
/home/sarah/oldLogs/units/personal.txt.gpg
sarah@james:~$ find / -type f -name data.txt 2>/dev/null
/home/sarah/logs/zmn/old stuff/-mvLp/data.txt
Step 2: Transfer Files via SCP
Transfer files from the remote server to your local machine (Remote → Local using scp):
General Syntax
scp USERNAME@REMOTE_IP:/REMOTE_FILE_PATH /LOCAL_PATH
Execution
# Transfer the encrypted file
scp sarah@10.48.150.61:/home/sarah/oldLogs/units/personal.txt.gpg .
# Transfer the wordlist
root@ip-10-48-135-245:~# scp sarah@10.48.150.61:/home/sarah/logs/zmn/”old stuff”/-mvLp/data.txt .
- Note: The period (.) represents the current directory.
- Local → Remote Reference: scp file.txt sajid@192.168.1.10:/home/sajid/
Step 3: Verify Local Directory Contents
root@ip-10-48-135-245:~# ls
CTFBuilder arm2b-contained.txt snap
Desktop data.txt test-reports
Documents full-suite.txt theHarvester-wrapper.orig
Downloads full-suite2.txt tools-final.log
Pictures go tools-postboot.log
Postman hash tools-run.log
Rooms install-th2.log tools-run2.log
Scripts msf-login.txt tools-run3.log
Templates neoreg_servers zap-gui-cat.txt
arm1-uncontained.txt personal.txt.gpg zapfix-fresh.txt
arm2-contained.txt reports zapfix-restored.txt
Step 4: Reverse the Wordlist with tac
tac data.txt > reversed.txt
How tac works:
यहाँ tac का काम समझना जरूरी है।
मान लीजिए data.txt में passwords इस तरह हैं:
apple
banana
orange
mango
grape
Running tac data.txt will reverse the line order:
grape
mango
orange
banana
apple
Step 5: Brute-Force GPG Hash Using John the Ripper
Use John the Ripper with the reversed wordlist to crack the GPG passphrase:
john –wordlist=reversed.txt –format=gpg hash
Output & Result:
root@ip-10-48-97-71:~# john –wordlist=reversed.txt –format=gpg hash
Using default input encoding: UTF-8
Loaded 1 password hash (gpg, OpenPGP / GnuPG Secret Key [32/64])
Cost 1 (s2k-count) is 65011712 for all loaded hashes
Cost 2 (hash algorithm [1:MD5 2:SHA1 3:RIPEMD160 8:SHA256 9:SHA384 10:SHA512 11:SHA224]) is 2 for all loaded hashes
Cost 3 (cipher algorithm [1:IDEA 2:3DES 3:CAST5 4:Blowfish 7:AES128 8:AES192 9:AES256 10:Twofish 11:Camellia128 12:Camellia192 13:Camellia256]) is 9 for all loaded hashes
Will run 2 OpenMP threads
Press ‘q’ or Ctrl-C to abort, ‘h’ for help, almost any other key for status
valamanezivonia (?)
1g 0:00:01:26 DONE (2026-09-12 15:03) 0.01156g/s 13.90p/s 13.90c/s 13.90C/s vigliacca..valamanezivonia
Use the “–show” option to display all of the cracked passwords reliably
Session completed
- Password found: valamanezivonia
Step 6: Decrypt and Read the File Content
Decrypt personal.txt.gpg using GPG with the cracked password:
root@ip-10-48-97-71:~# gpg personal.txt.gpg
gpg: WARNING: no command supplied. Trying to guess what you mean …
gpg: AES256.CFB encrypted data
gpg: encrypted with 1 passphrase
File ‘personal.txt’ exists. Overwrite? (y/N) n
Enter new filename: personal1.txt
Read the decrypted content:
root@ip-10-48-97-71:~# cat personal1.txt
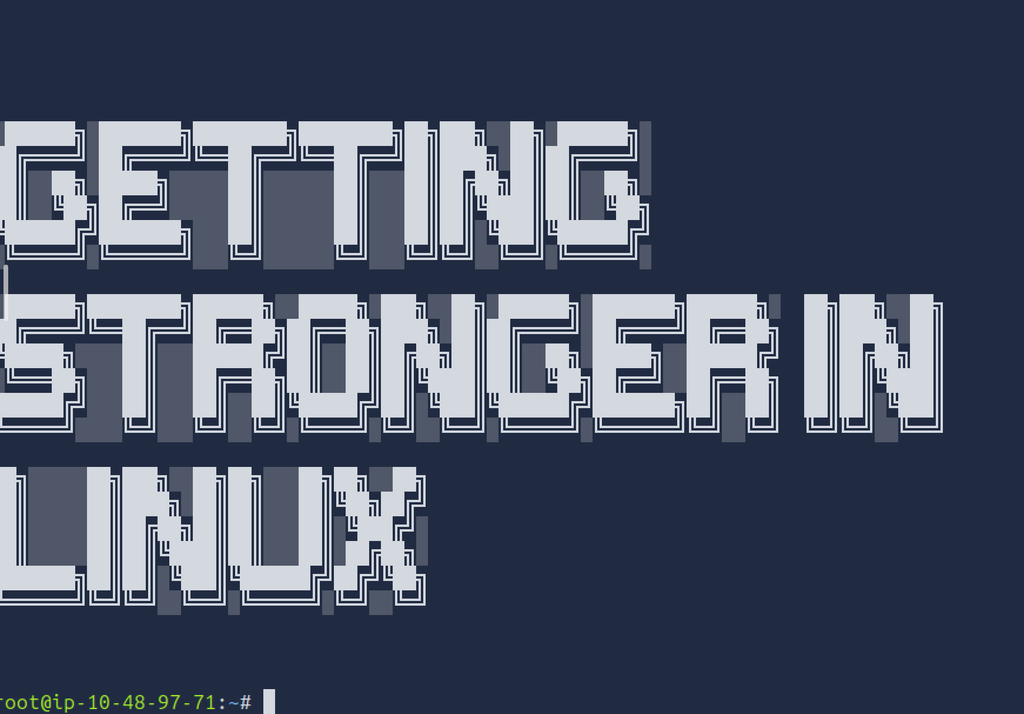
getting stronger in linux
Decrypted content: getting stronger in linux